Table of Contents
You probably don’t have a complete picture of your firm’s IT environment. You know what works and what breaks. You don’t always know what’s outdated, what’s exposed, or what would happen if something failed at the wrong moment.
That’s what a law firm IT assessment surfaces, and it’s the first thing to ask for if you’re weighing a move to managed IT.
If you’ve been offered one, it’s reasonable to wonder what you’re actually agreeing to. Whether it will disrupt the firm, who needs access to what, and whether you’ll get something useful at the end, or just a sales pitch with a more official-sounding name.
A good assessment answers those questions and gives you something actionable whether you move forward with the provider or not.
There are two ways in: a full review by an IT provider with access to your systems, or a self-check you run first to see where your firm stands.
What Is a Law Firm IT Assessment?
A law firm IT assessment should evaluate your systems, including hardware, network infrastructure, Microsoft 365, cybersecurity controls, backups, user access, legal software, and IT documentation.
The goal is to identify risks, gaps, outdated systems, recurring support problems, and practical improvements.
The assessment should go beyond a basic network scan.
A generic IT review might check devices, servers, firewalls, and antivirus. A law firm IT assessment should also consider how attorneys and staff work:
A useful assessment should also be understandable to firm leadership.
The findings should explain what was found, why it matters, and what should happen next, so the managing partner or administrator doesn’t have to translate a technical export into business decisions.
Why Law Firms Get an IT Assessment
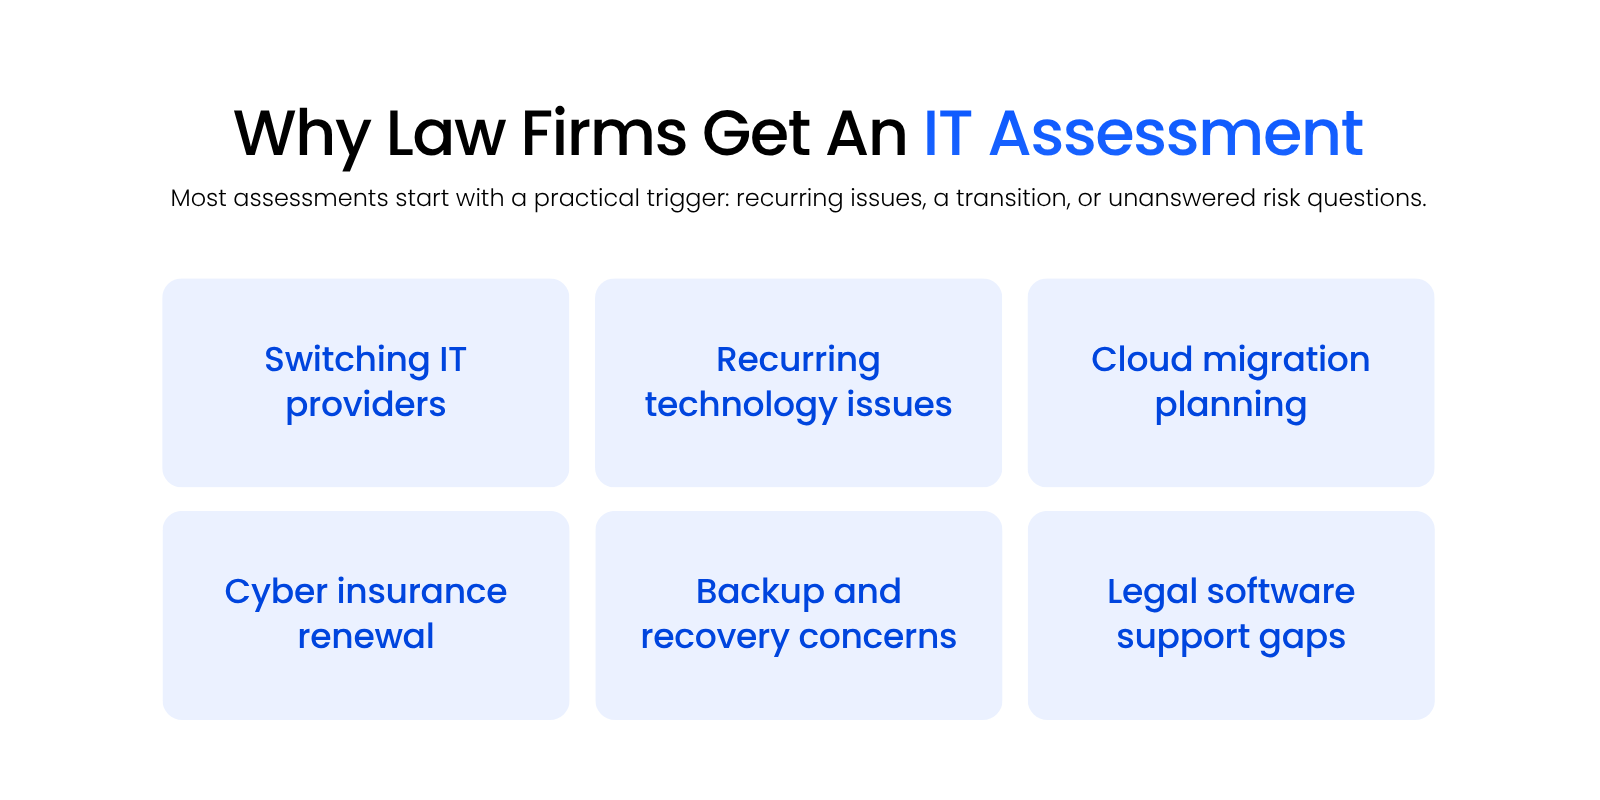
Firms get an IT assessment when something prompts the question: day-to-day IT frustration, a transition like a provider switch, or a risk question nobody can answer with confidence.
Sometimes it’s frustration. The firm keeps dealing with slow computers, unreliable remote access, recurring Outlook issues, scanner problems, or legal software errors that no one fully explains.
Sometimes it’s a transition. The firm may be switching IT providers, moving away from an on-premise server, planning a cloud migration, or trying to figure out what its current provider has actually been managing.
Other times, the trigger is risk. A cyber insurance renewal may require clearer documentation.
A client may ask about the firm’s security posture. Leadership may realize that no one has a confident answer to basic operational questions.
Signs Your Firm Is Due for an IT Assessment
Check your firm against these signs. Each one is something a managing partner can confirm today.
A full third-party review was still the exception in 2023. The ABA’s 2023 Cybersecurity TechReport found that “29% of respondents reported that their firms had a full security assessment performed by a third party.”
Solo lawyers were at the low end, “with only 21% responding that their firm had a security assessment conducted by a third party.” The same ABA report says: “Some cyber insurance carriers may require that a third party perform an assessment.”
What pushes a firm to act is often a questionnaire from a client or a cyber insurer. Not being able to answer one honestly is what shows a firm where its gaps are.
A five-attorney firm with Microsoft 365, a practice management platform, local scanners, and a few remote staff members still has a lot of systems to keep track of. So does a 40-user firm with multiple offices, legacy billing software, document management, and a mix of in-office and remote users.
The assessment brings those pieces into view.
What Gets Reviewed During a Law Firm IT Assessment?
A thorough law firm IT assessment reviews the systems attorneys and staff rely on every day, along with the security, backup, and support structure behind them.
This is where a legal-specific assessment should separate itself from a generic IT review.
A basic assessment may look at devices, firewalls, and network settings. A law firm IT assessment should also review legal software, matter data, Microsoft 365 configuration, backup coverage, user access, documentation, and the systems that support confidential client work.
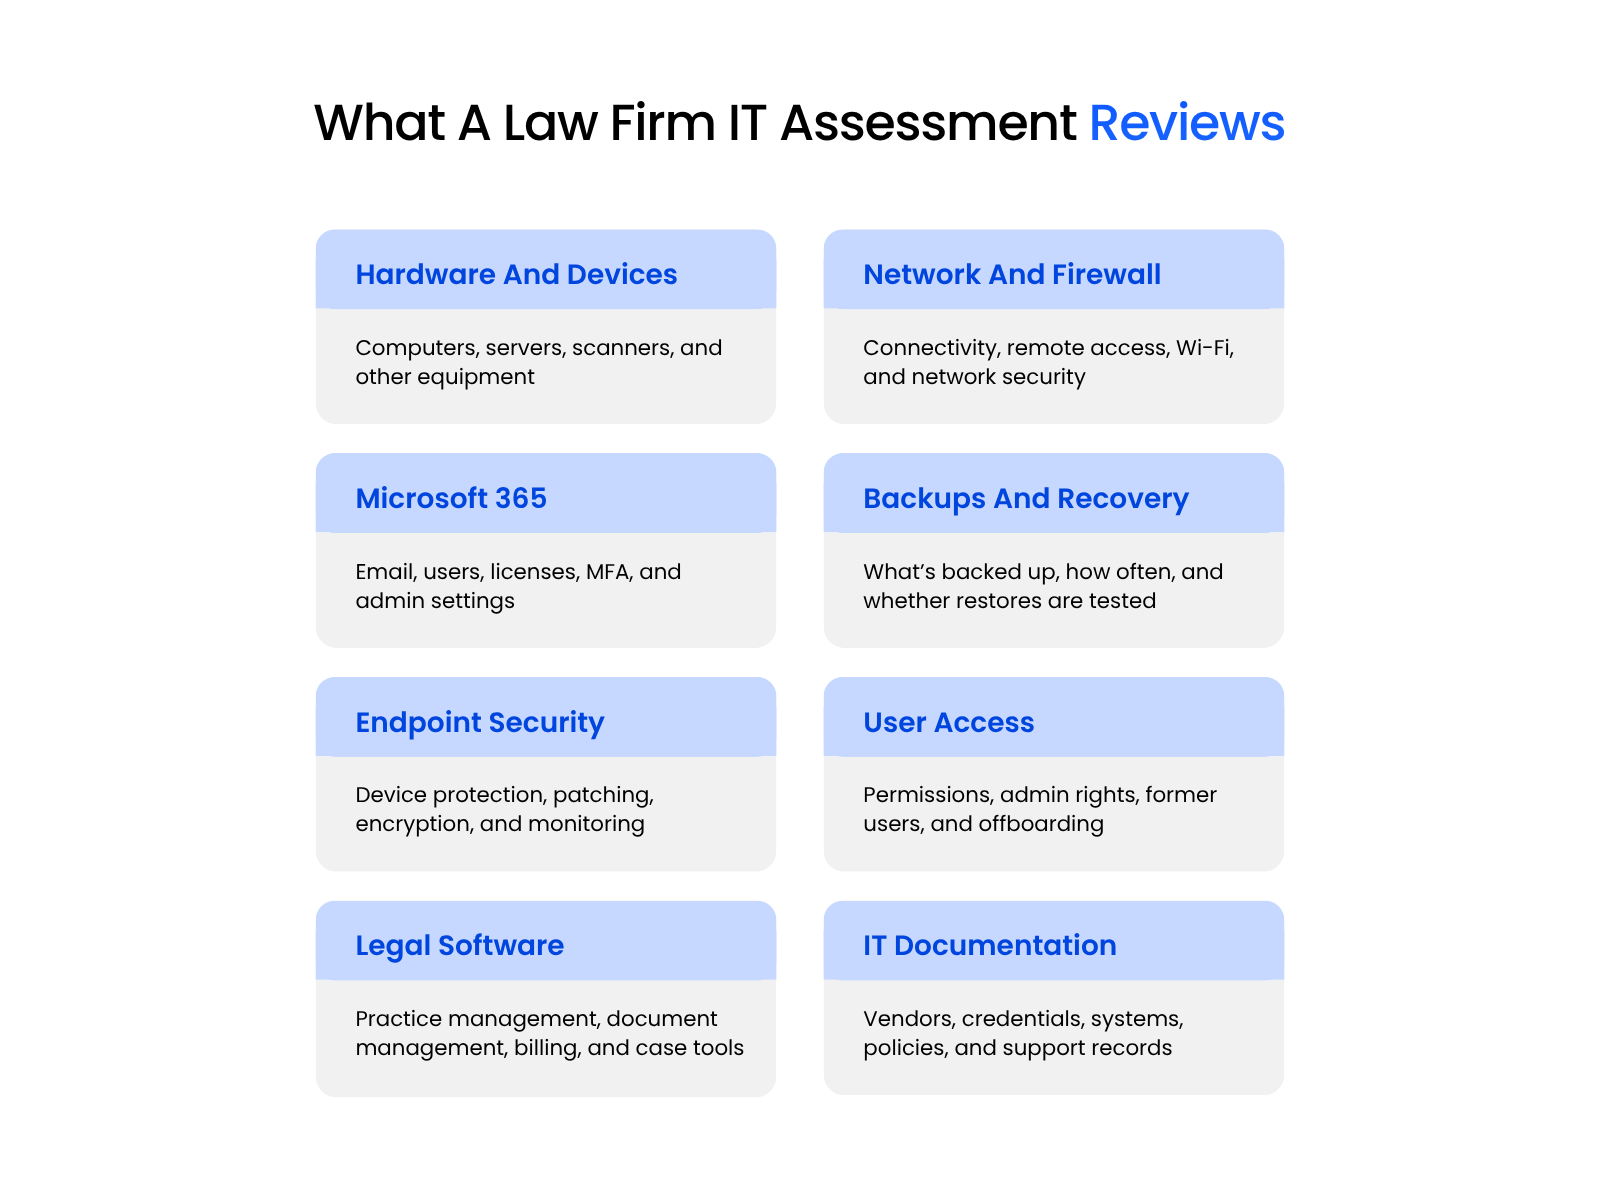
A strong assessment usually reviews eight core areas:
Hardware and Device Inventory
The assessment should start with the devices the firm uses: desktops, laptops, servers, printers, scanners, mobile devices, and aging equipment still connected to the environment.
The provider is checking what exists, what’s outdated, what’s unmanaged, and what may no longer be supported. That includes attorney laptops, staff workstations, shared scanning stations, home-office devices, and any machine that still has access to firm systems.
This gets practical fast:
Those issues affect the firm’s ability to work securely and consistently.
Network Infrastructure and Firewall
The assessment should review the firm’s firewall, internet setup, Wi-Fi, switches, remote access, and overall network design.
The provider is checking whether:
This is especially important for firms that still rely on a fragile virtual private network (VPN), exposed remote desktop access, or a server closet that everyone hopes will keep behaving.
Network reliability has a direct operational cost. If attorneys can’t reach files, email, billing systems, or legal software when they need them, the technology problem quickly becomes a client-service problem.
Microsoft 365 Configuration and Security
Microsoft 365 is often one of the most important systems in a law firm. It touches email, calendars, Teams, SharePoint, OneDrive, identity management, device access, and user permissions.
A good assessment should review:
It should also look at whether Microsoft 365 supports the firm’s workflow. A messy setup can create confusion over where documents live, who can access shared files, whether former employees still have access, and whether email security is configured properly.
For many firms, Microsoft 365 is where productivity and risk meet. It runs email, identity, and collaboration, which means a weak configuration can create problems across the entire firm.
Backup Systems and Restore Verification
Backups answer a simple question: if something breaks, can the firm actually recover?
The assessment should review:
That includes servers, workstations, Microsoft 365, legal software data, and matter files.
The key word is restore.
A backup that has never been tested is more of an assumption than a recovery plan. Nobody knows whether that assumption holds until a server fails, ransomware hits, files are deleted, or a cloud system doesn’t retain the data the firm thought it did.
A good assessment should make the backup picture concrete: what’s protected, what isn’t, how fast the firm could recover, and what data might be harder to restore than leadership expects.
Endpoint Security and Patch Status
The assessment should review the security posture of the devices that attorneys and staff use every day.
That usually includes:
This is especially important for firms with hybrid or remote users. A laptop that accesses client files from court, home, a hotel, or a client site should still be protected, patched, and accounted for.
The firm shouldn’t have to guess which devices are secure and which ones are missing patches or no longer report to anyone.
User Access Controls and Offboarding
User access review answers a basic but important question: who can access what?
The provider should look for:
User access is tied directly to confidentiality. A paralegal, attorney, billing user, outside consultant, and former employee shouldn’t all have the same level of access.
The assessment should help the firm see whether access matches each person’s role and whether the offboarding process actually removes access when someone leaves.
This kind of issue is easy to miss. A former employee may be removed from payroll and email forwarding, but still have access to a file share, Microsoft 365 group, legal software account, or remote access tool.
Legal Software Health and Support Coverage
This is one of the biggest differences between a generic IT assessment and a law firm IT assessment.
The provider should review the systems where legal work happens, including practice management, document management, billing, accounting, case management, and legal-specific cloud platforms. Depending on the firm, that may include Clio, NetDocuments, iManage, Worldox, Tabs3, ProLaw, PCLaw, Time Matters, QuickBooks, or other software the firm depends on.
The assessment should check whether:
This is where law firm experience shows. A generalist provider may be comfortable with laptops, routers, and Microsoft 365 and still not understand why a Worldox indexing issue, a Tabs3 workstation problem, a ProLaw performance complaint, or a scanner-to-document-management workflow can derail a normal workday.
Documentation and IT Records
Your firm’s technology environment shouldn’t depend on what one person remembers.
The assessment should review whether the firm has current documentation for:
Poor documentation creates dependency. It makes changing IT providers harder, slows down urgent support, and complicates insurance questions.
This matters during everyday support, too. If no one knows who manages the domain, where firewall credentials are stored, which vendor supports the phone system, or what backup product protects the server, every issue takes longer than it should.
Good documentation gives the firm more control over its environment.
How Long Does a Law Firm IT Assessment Take?
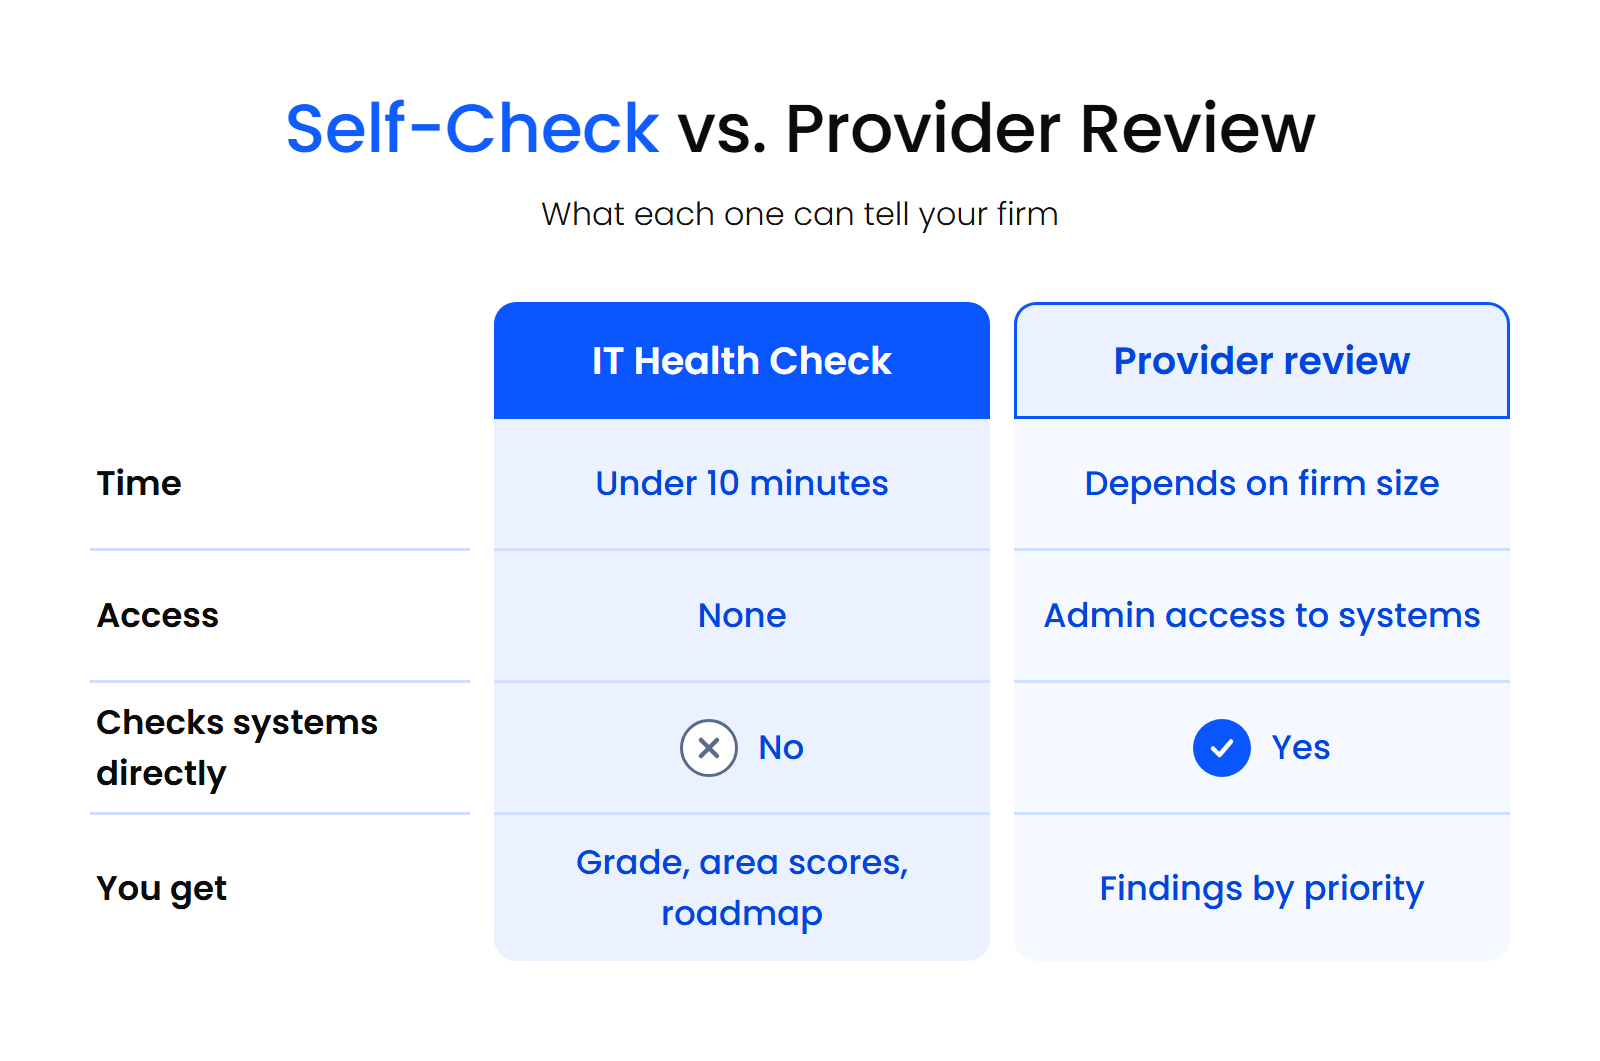
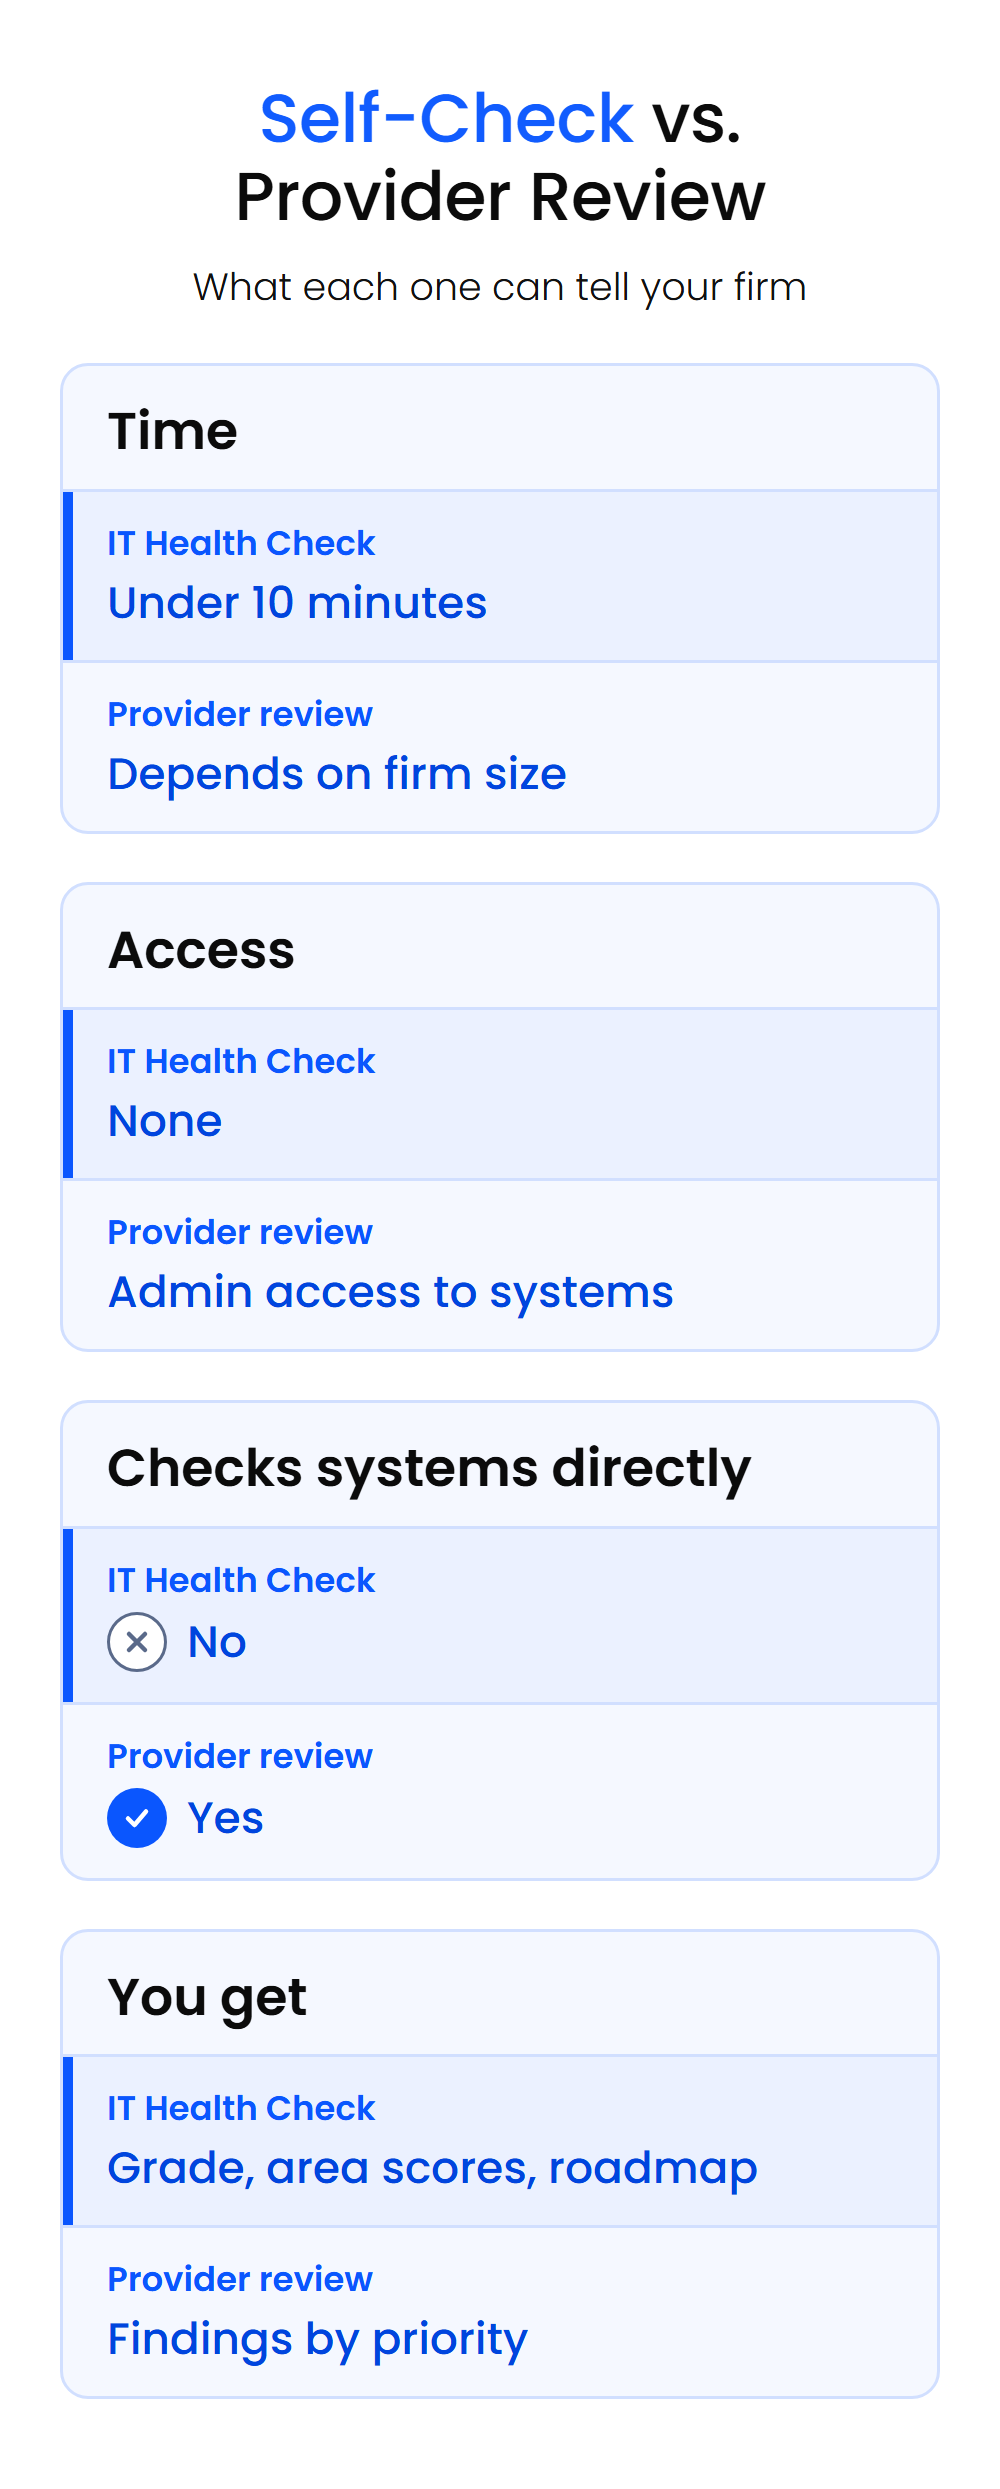
How long a provider’s IT assessment takes depends on your firm’s size, its systems and how quickly you can give access, while a self-check like the IT Health Check takes under 10 minutes and needs no access to your systems. A provider review needs both access and a follow-up conversation.
More users and offices, more servers and legal applications, remote staff, and layered security tools all add review time, and so does slow access or slow answers to follow-up questions. Ask the provider for a timeline before the review starts.
The first conversation should cover why the firm is looking now, what software holds its work, how much data sits in active and archived matters, and how the firm is shaped: users, offices, remote staff, of counsel, and anyone working overseas. Those answers show whether the firm’s IT setup fits how the firm works.
The firm usually needs to:
Attorneys and staff typically don’t need to stop working.
A provider review needs administrative access to what it reviews, such as the Microsoft 365 admin center, the firewall, the backup console, and your legal applications’ admin settings. Nobody can confirm a backup works from the outside, because checking it means getting into the backup software itself.
What Are the Steps in a Law Firm IT Assessment?
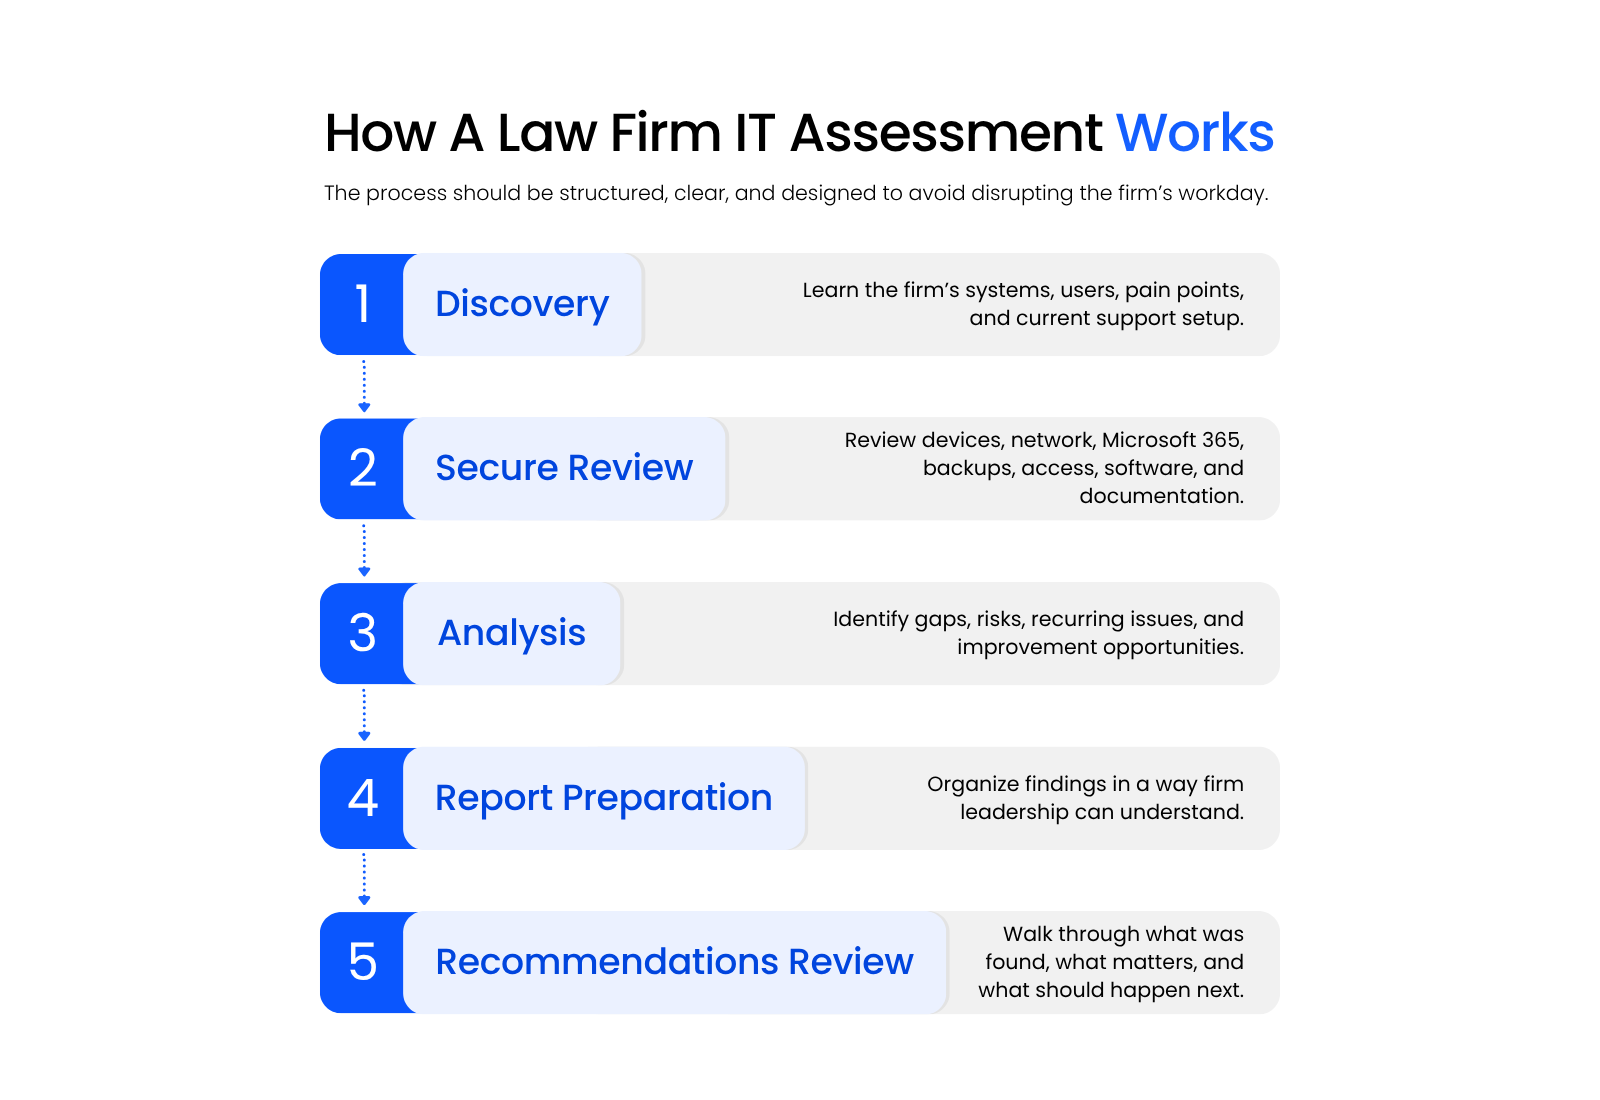
A typical assessment process looks like this:
The assessment should fit around the firm’s workday.
A good legal IT provider should be able to explain what access is needed, what will be reviewed, who needs to be involved, and what attorneys and staff can expect.
What You Get at the End: The Assessment Report
A useful IT assessment ends with findings firm leadership can act on, written up as a report, scored by area, or both. The report is where the assessment proves its value or fails to.
A useful report should be written for firm leadership, not only for technical staff. It should explain what was reviewed, what was found, why each finding matters, and what the firm should do next.
A good law firm IT assessment report should include:
It shouldn’t feel like a 50-page export from a scanning tool. It also shouldn’t be so vague that every recommendation sounds the same.
For example, a weak report might say:
“Security should be improved.”
A stronger report would say:
“MFA is not enforced for three users with access to email and firm files. This should be corrected immediately because compromised credentials can create unauthorized access to confidential firm information.”
One statement sounds serious but gives the firm no clear action. The other tells leadership what was found, why it matters, and what to do about it.
What Does a Scored Assessment Tell You?
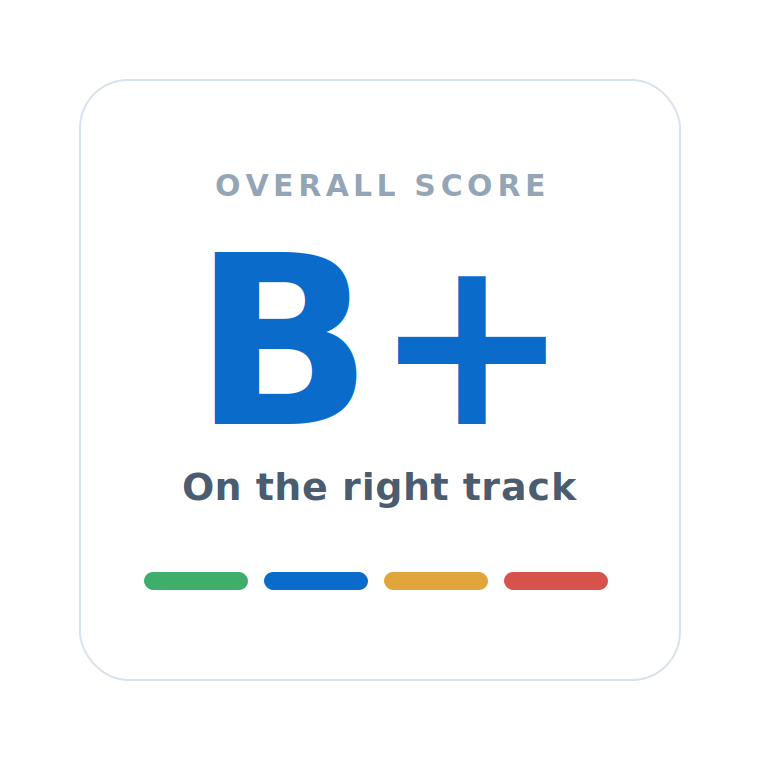
Some assessments grade your firm by area as well as, or instead of, writing a narrative report. The IT Health Check returns this kind of result: an overall letter grade, a percentage for each area, and a prioritized roadmap.
A score built from your own answers tells leadership where to look first. Proving that a backup restores, or that a firewall is configured well, takes someone checking those systems directly.
The report should help the firm make decisions about what to fix, whether its current IT support for law firms is adequate, and what changes are worth prioritizing. It shouldn’t just make the provider sound necessary.
Is a Free IT Assessment Just a Sales Pitch?
Sometimes, yes.
An IT provider that offers a free assessment is hoping your firm will become a client. There’s nothing wrong with that as long as the assessment is real.
The question is whether the process gives your firm useful findings regardless of what you decide next.
A genuine assessment reviews the actual environment, identifies specific issues, explains the practical impact, and gives the firm something it can use. A surface-level assessment skips the deeper review and jumps quickly to a proposal.
A free assessment can be a reasonable first step in choosing a legal IT partner if you hold it to a real standard.
If the provider can’t explain what they reviewed, what they found, and why it matters for a law firm, the assessment probably wasn’t thorough enough.
A Quick Self-Check: Questions to Answer Before an IT Assessment
You can check your firm’s IT before you talk to any provider by answering the yes/no questions below. The managing partner or administrator can answer them today without logging into anything, and every “no” or “I don’t know” marks an area a full assessment should look at.
- 1Is MFA enforced for every account that can reach email or firm files, staff included?
- 2Can you name the last time someone restored a file from backup, rather than checking that the backup ran?
- 3Does your backup cover matter files, Microsoft 365, and your legal software’s data?
- 4Could you list every person with admin access to Microsoft 365?
- 5Does your firm control which personal phones and laptops can reach firm email?
- 6Does every laptop that opens client files get security updates and report to someone who checks it?
- 7When someone leaves, does your firm confirm their access is removed from every system, legal software included?
- 8Is your legal software on a version its vendor still supports?
- 9Are your firewall and remote access setup documented somewhere the firm can find them?
- 10If an outside provider or consultant holds admin credentials, are they written down somewhere the firm controls?
A self-check catches what you already know to ask. A provider review finds what nobody on staff knew to look for, because it checks the systems themselves.
When we onboard a new law firm client, the gaps we find most often are missing MFA and staff using their own devices with no control over which devices can connect.
What to Do with the Findings
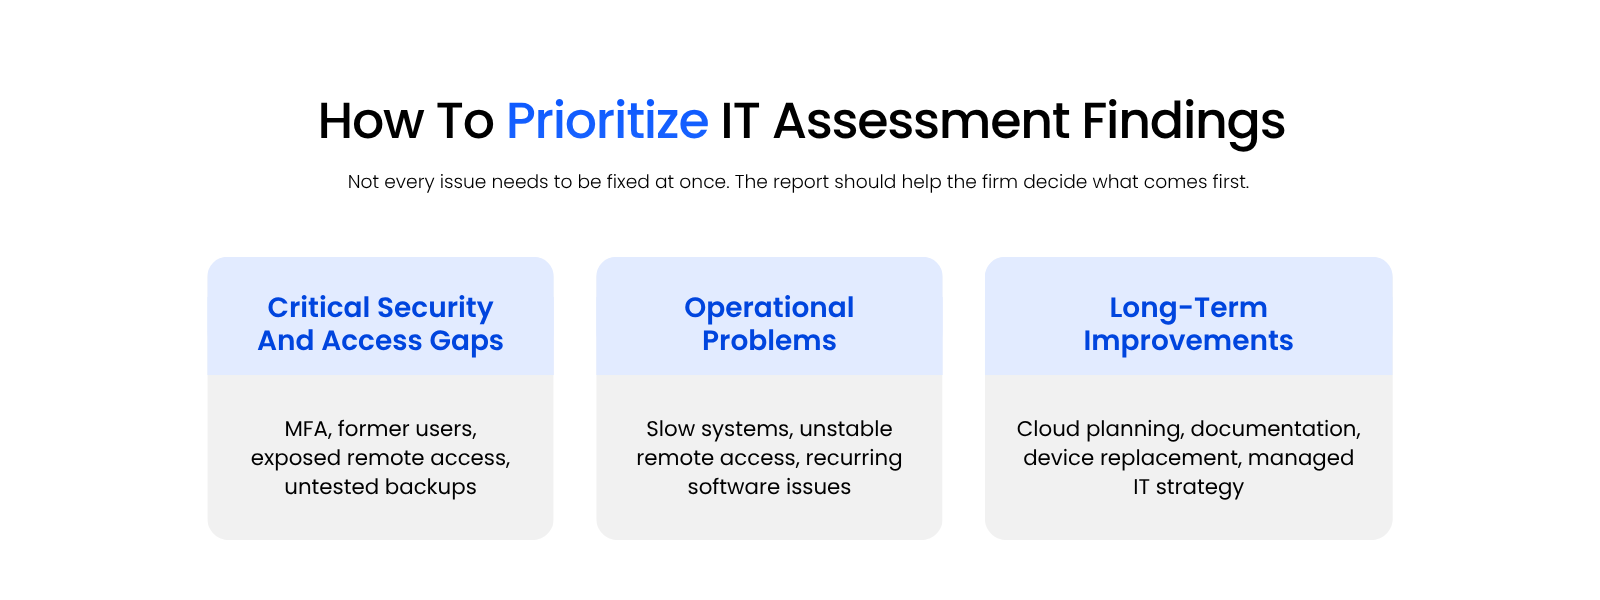
Work through the findings in priority order: critical security and access gaps first, then the operational problems slowing the firm down, then longer-term improvements. An IT assessment is only useful if the firm acts on it.
A good report should help leadership sort the findings into a practical order, since not every finding needs to be fixed at once.
Start with Critical Security and Access Gaps
The first priority should be anything that creates immediate risk: missing MFA, former employee accounts, exposed remote access, unprotected devices, unsupported systems, or backups that can’t be restored confidently.
These issues affect security, continuity, and access to client information. They shouldn’t sit in a “future improvements” folder for six months.
Examples might include:
Then Fix the Operational Problems Slowing the Firm Down
Next, look at the issues that keep costing the firm time: unstable internet, recurring Microsoft 365 problems, slow workstations, unreliable VPN access, legal software performance issues, or support processes that leave attorneys and staff waiting too long.
This is where the assessment traces day-to-day frustration to root causes. When everyone complains about the document system, the cause may be an underpowered server, an unstable VPN, an inconsistent workstation setup, or an application that’s no longer properly supported.
Managed IT for Law Firms: What It Includes, Why It Matters, and How to Choose the Right Provider:
Learn what managed IT should cover for law firms, including help desk support, Microsoft 365, security, legal software support, and long-term planning.
Examples might include:
Plan Longer-Term Improvements with a Real Sequence
After the urgent and recurring issues are clear, the firm can do its longer-term technology planning with more confidence.
That might include cloud migration, Microsoft 365 cleanup, documentation improvements, legal software upgrades to supported versions, device replacement, better onboarding/offboarding processes, or a stronger managed IT model.
Examples might include:
The key is sequence. A good assessment helps the firm decide what needs immediate attention, what should be planned, and what can wait.
Start with Uptime Legal’s Free IT Health Check
Uptime Legal’s IT Health Check is a free self-assessment built for law firms: 20 questions, under 10 minutes, and a score for each area of your firm’s IT.
It scores these areas:
You get back an overall grade, a score for each area, and a prioritized roadmap.
Because the Health Check runs on your answers, it can’t test a restore or read your firewall configuration. It shows you where to look in under 10 minutes, and a review with access to your systems confirms what’s actually there.
Run the IT Health Check this week, with whoever knows your systems best beside you.
Then read your lowest-scoring areas first. If security or backups are among them, have someone check those systems directly before you rely on the score.
Get a consultation to talk through what your score means for your firm. If you’d rather hand the fixes and the ongoing work to us, Uptime Manage, our managed IT service for law firms, takes that on.
WHAT’S NEXT
Frequently Asked Questions

Uptime Legal’s Technology Solutions
Cloud, software, IT, and document management built for today’s law firms.